
Regulations & Frameworks
-
Why Compliance Leaders Need a Seat at the Executive Table (And How Unified Data Gets You There)
Compliance leaders earn executive credibility through unified data. Learn why compliance belongs at the boardroom table and how to get there.
-
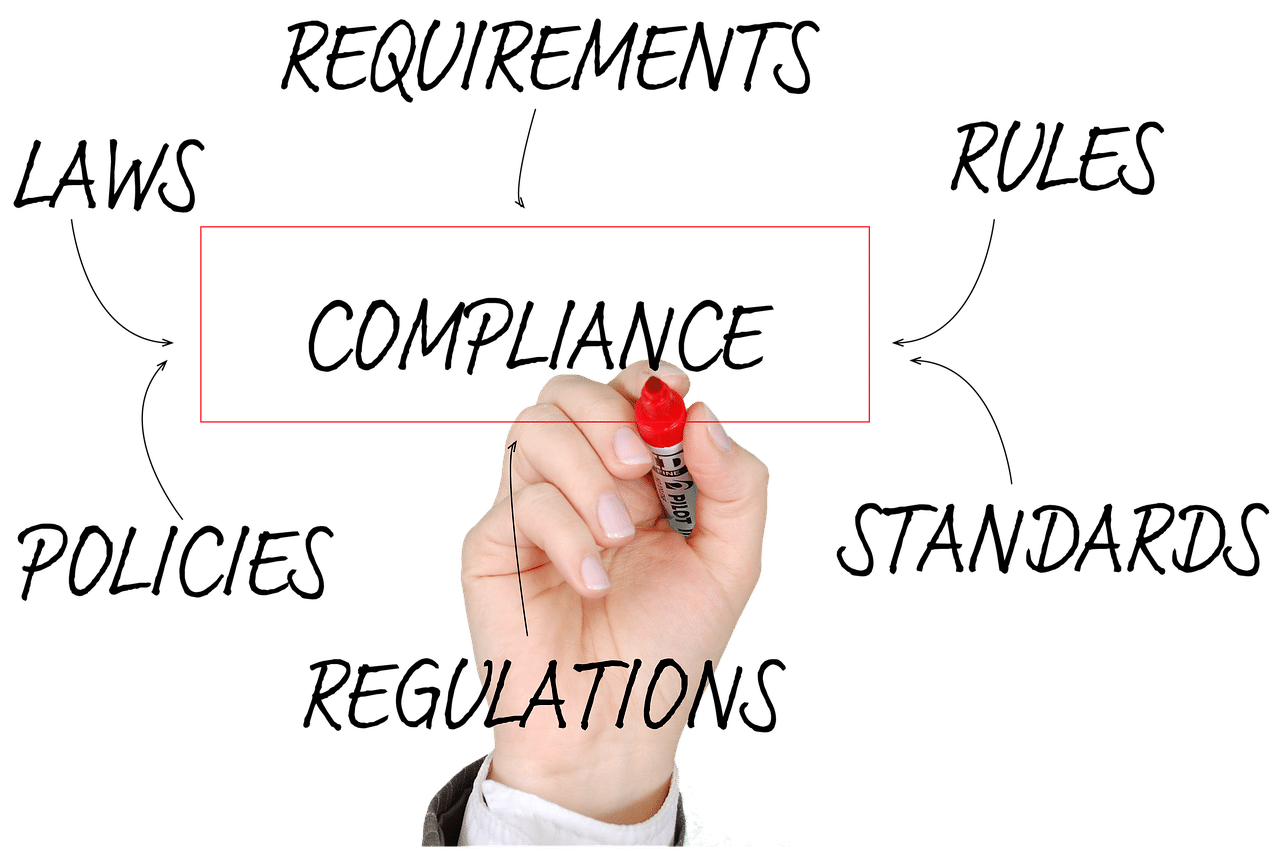
Framework Overlap Is Killing Your Compliance ROI
70% of organizations waste compliance resources managing overlapping frameworks. Learn how to map shared controls and improve your ROI.
-
Mapping Multiple Frameworks into a Unified Compliance Program
Compliance teams waste resources managing multiple frameworks with disconnected tools. Learn how unified GRC technology eliminates duplicated work and strengthens collaboration across teams.
-

Connecting the Dots: How Compliance Frameworks and TPRM Strengthen the SLED Supply Chain
Learn how NIST RMF helps SLED organizations manage third-party risks, strengthen vendor oversight and simplify multi-regulatory compliance.
-
CMMC Phase II May Be Paused. Your Compliance Program Shouldn’t Be.
CMMC Phase II audits paused, but NIST 171 requirements remain. See why strengthening compliance now positions you for whatever comes next.
-
Evaluating Alternative Business Solutions: A Governance Framework for Change
Evaluate business solutions with governance at the center. Reduce risk and build stakeholder confidence in your transformation decisions.
-
The Compliance Challenge: Managing GDPR, CCPA and Everything in Between
Compliance management software helps teams centralize controls, reduce manual work, and stay ahead of GDPR, CCPA, and evolving regulations.
-
A Looming Challenge: How Healthcare Risk Management Must Stay Connected in a Cyber Crisis
Ryan Redman JD CHC CHPC, Onspring’s product marketing manager, explains why fragmented risk data leaves healthcare CISOs blind to dependencies and how a centralized GRC approach keeps response fast and accountable during a cyber incident.
-
Regulatory Change Management: The Compliance Gap You Can’t Ignore
Regulatory changes create compliance gaps most teams never see coming. Learn how to build a process that keeps your program audit-ready.
-
Integrating NIST Supply Chain Risk Management into SLED Compliance Programs
Integrate NIST supply chain risk management into SLED compliance programs to strengthen vendor oversight and operational resilience.
-
How to Choose the Right Risk Strategy for Different Types of Risk
Choose the right risk strategy using likelihood and impact to improve risk visibility and align with GRC best practices.
-
The Next Evolution of Healthcare Cybersecurity: Navigating the Proposed Changes to the HIPAA Security Rule
HIPAA Security Rule updates introduce stricter controls, MFA, and continuous risk analysis—what healthcare leaders must do to prepare.


